
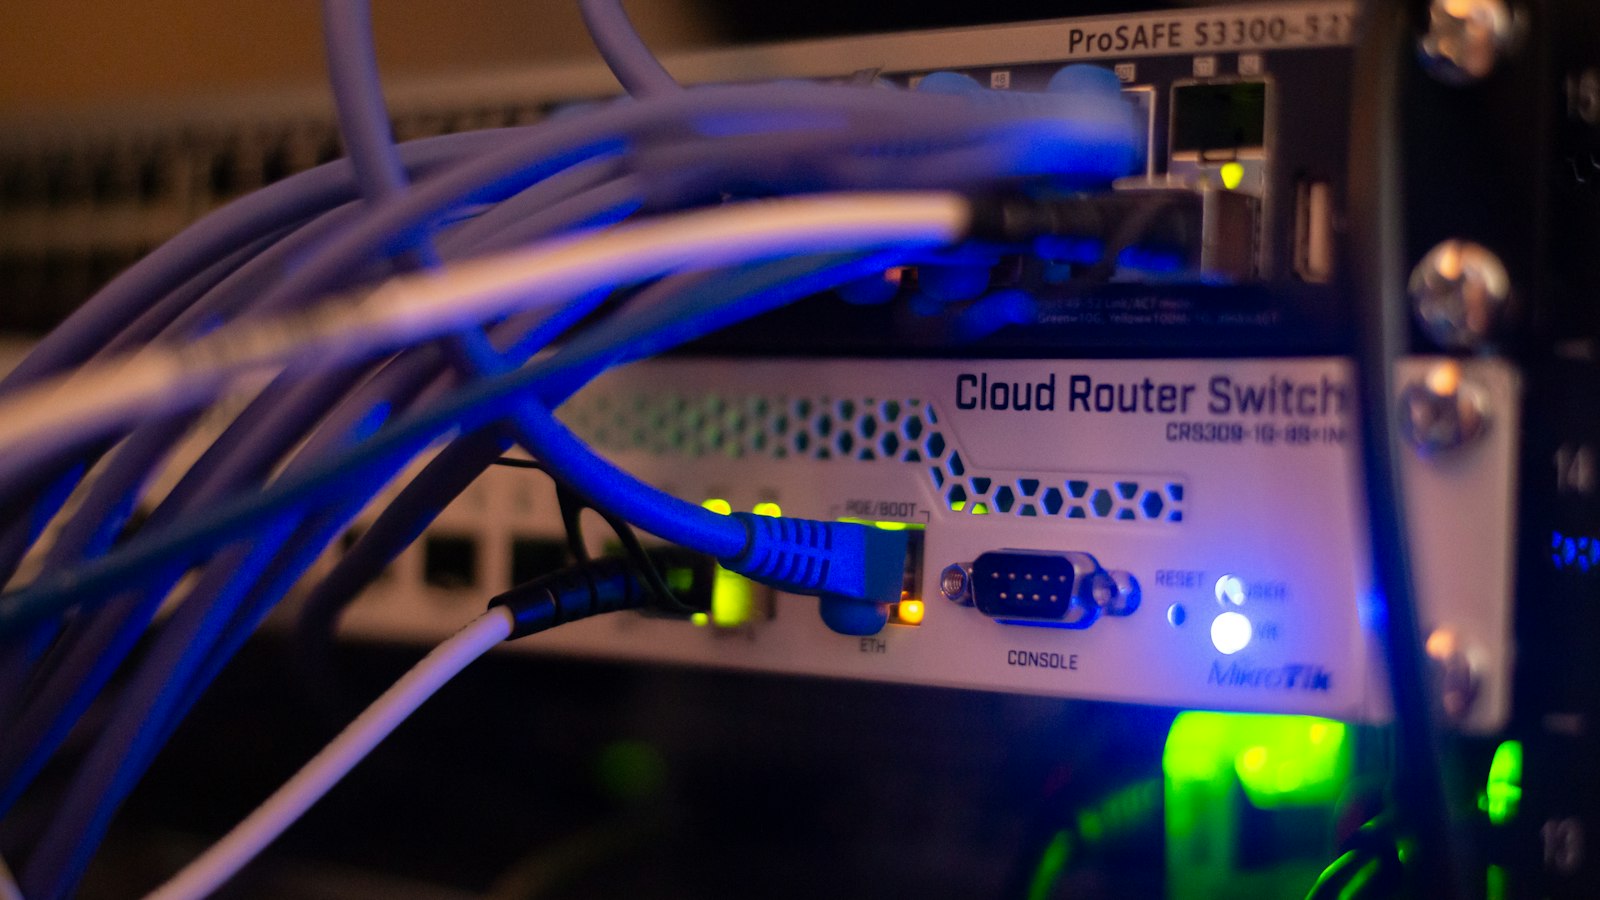
Why does multi-branch IT get harder the more you grow?
Because every branch that stands up its own IT independently adds a new, slightly different environment to support — and none of these differences show up as a problem until something breaks or gets exploited. A retail chain that opens branch six with a different router brand, a different POS vendor, and a different local IT contractor than branch two isn't wrong on any single decision. But multiply that across ten, twenty, fifty branches, and you don't have a business with consistent IT — you have dozens of small, disconnected IT environments that happen to share a brand name. The businesses that scale smoothly past this point standardize deliberately. The ones that don't spend years untangling inconsistency they didn't realize they were accumulating.
This matters most for businesses where consistency isn't just an efficiency question but a compliance and risk one — NBFCs handling financial data and regulatory reporting requirements, retail chains processing payment card data across every location, and franchises where brand consistency and centralized oversight are part of the business model itself.
What does a centralized helpdesk actually solve?
The obvious answer is faster support — one ticketing system, one number to call, consistent response times regardless of which branch is having the issue. But the less obvious and more valuable benefit is pattern visibility. When every branch handles its own IT informally, a recurring issue — a specific POS terminal model that keeps failing, an ISP with unreliable uptime in a particular region, a misconfigured software update causing problems — shows up as N separate, disconnected complaints instead of one clearly identifiable pattern. A centralized helpdesk with a shared ticketing history turns "branch 14 called again about the printer" into "this printer model has failed at four branches this quarter" — which is the difference between reactive firefighting and a fixable root cause.
Centralizing also removes a dangerous single point of failure common in smaller multi-branch operations: the local "person who's good with computers" who holds undocumented knowledge about how that branch's systems are configured. When that person leaves, the branch often loses its only institutional IT knowledge along with them.
“”
Why standardized hardware pays for itself
Standardizing hardware — a small, approved set of configurations per role (branch workstation, POS terminal, network router, branch server) — isn't about uniformity for its own sake. It compounds into real operational savings:
- Faster support. A helpdesk troubleshooting a known, standard configuration resolves issues faster than one guessing at whatever equipment a branch happened to acquire locally.
- Cheaper procurement. Buying a known set of SKUs at volume is materially cheaper than ad hoc local purchases at each new branch, and it simplifies budgeting for hardware refresh cycles.
- Consistent patching and security. Security patches, firmware updates, and end-of-life tracking are dramatically simpler across a known, small set of hardware than across dozens of different models with different vendors and different update cycles.
- Predictable disaster recovery. When hardware is standardized, replacing a failed unit at any branch is a known, fast process — swap in a pre-configured standard unit — rather than a custom troubleshooting exercise each time.
What does a unified network and security policy actually mean?
It means every branch meets the same security baseline, enforced centrally — not documented in a policy PDF and hoped for locally. In practice this covers a consistent VPN or SD-WAN setup connecting every branch to core systems securely, uniform wifi security configuration (not "whatever the local router's default was"), centrally managed firewall rules, and consistent patch management pushed from a central point rather than relying on each branch to remember.
The risk this addresses is specific and common: attackers and automated scanning tools don't need every branch to be vulnerable — they need one. A single branch with a weak or default wifi password, an unpatched router, or a forgotten VPN misconfiguration can become the entry point that compromises data or systems across the whole business, even if every other branch is properly secured. This is why security policy for a multi-branch business has to be a centrally enforced baseline, not a set of local best-effort implementations.
How cloud infrastructure fits into this
Moving core systems — point-of-sale data, inventory, customer records, line-of-business applications — to centrally hosted cloud infrastructure rather than local per-branch servers is usually the single highest-leverage move a multi-branch business can make. It means every branch is working against the same live data instead of maintaining its own silo that needs manual reconciliation. It makes centralized reporting possible without stitching together data from dozens of disconnected local systems. And it dramatically simplifies disaster recovery — if a branch's local hardware fails or is stolen, the actual business data isn't lost with it, because it was never only stored there.
What this looks like for NBFCs specifically
Non-banking financial companies carry a compliance dimension that a typical retail chain doesn't — regulatory reporting requirements, audit trails for financial transactions processed at every branch, and often specific data localization or retention rules depending on jurisdiction. For an NBFC with multiple branches, standardized infrastructure isn't just an efficiency play, it's what makes regulatory reporting and audits tractable in the first place. If every branch is running slightly different systems with different logging practices, producing a consistent, auditable record across the whole organization becomes a manual reconciliation exercise every reporting cycle instead of a query against a consistent, centralized system. Getting infrastructure standardized early is one of the highest-leverage things an NBFC can do to keep compliance overhead from growing linearly with branch count.
What this looks like for retail chains and franchises
For retail chains and franchises, the standardization conversation is more often about brand consistency and payment security than regulatory reporting, but the underlying logic is the same. A customer's experience — and a franchise's PCI DSS compliance posture for card payments — shouldn't depend on which specific location they're visiting. Franchise models in particular benefit from centralizing IT decisions at the franchisor level: individual franchisees usually don't have the expertise or incentive to independently maintain a strong security posture, and a single weak franchisee location becomes a liability for the whole brand if a breach or outage traces back to inconsistent local IT. Centralized hardware standards, a shared helpdesk, and franchisor-enforced network policy turn IT from a per-location variable into a consistent part of what the franchise agreement actually delivers.
Getting started without a full rebuild
You don't need to rip out and replace every branch's IT simultaneously. A practical sequence that works for most multi-branch businesses:
- Audit what's actually running at each branch — hardware, network config, local vs. cloud systems — so you know your actual starting point, not your assumed one.
- Define the standard — the approved hardware set, the network and security baseline, the centralized helpdesk process — based on what the audit reveals and what compliance or brand requirements demand.
- Migrate opportunistically, prioritizing the highest-risk branches (oldest hardware, weakest security posture) first, and applying the standard to every new branch going forward so you're not adding to the inconsistency while you fix the existing backlog.
We help NBFCs, retail chains, and franchise operators design and roll out exactly this kind of standardized infrastructure through our managed IT services and network setup & management offerings — starting with the audit, because you can't standardize what you haven't mapped first.
FAQs
Frequently asked questions
Written by
Partha Sarathi Ghosh
Founder & Engineering Lead, DevOrbital
Partha leads DevOrbital, where his team has elevated 50+ businesses across MVP development, AI agents, custom software, and growth. He writes about the hidden mechanics of getting AI-generated code into production, MVP scope discipline, and the architecture decisions founders make too late.
Keep reading